

A member of the Kosli Customer Success team will give you:
- The primary and secondary AWS regions your instance uses.
- The Kosli AWS account ID (
<<kosli-account-id>>) to grant access to in the key policy.
Prerequisites
- An AWS account you will use to own the KMS keys.
- Permissions in that account to create and manage KMS keys.
- The primary/secondary regions and the Kosli account ID (
<<kosli-account-id>>) from a member of the Kosli Customer Success team.
Choose the key shape
AWS does not permit multi-region KMS keys whose key material lives in a custom key store.- If your key material can live in KMS (generated or imported), create one multi-region key in the primary region and replicate it into the secondary region. This is the path described below.
- If your policy requires an AWS CloudHSM key store or an external key store for key material, create two single-region keys — one in each region. See Single-region keys for the differences.
Create the primary key
- Sign in to the AWS account that will own the keys and open the AWS KMS service.
-
KMS is a regional service. Switch the console to the primary Kosli region.
-
In the left-hand menu, select Customer-managed keys.
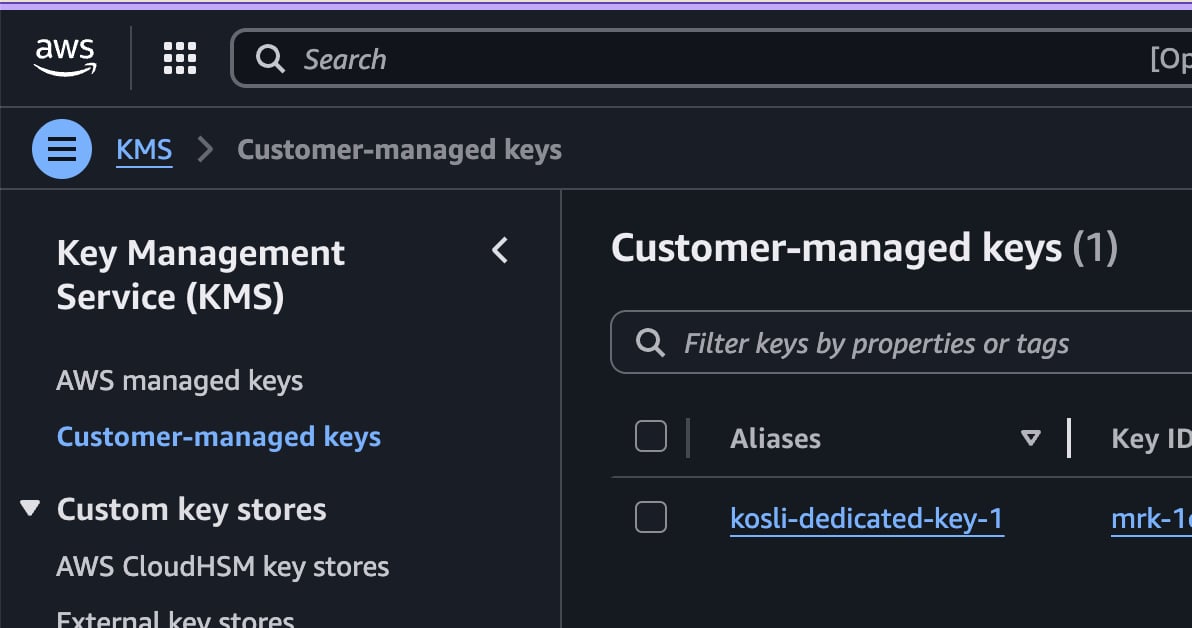
- Click Create key in the top right to start the wizard.
Step 1 — Configure the key
- Key type: Symmetric
- Key usage: Encrypt and decrypt
- Expand Advanced options and, under Regionality, select Multi-region key.
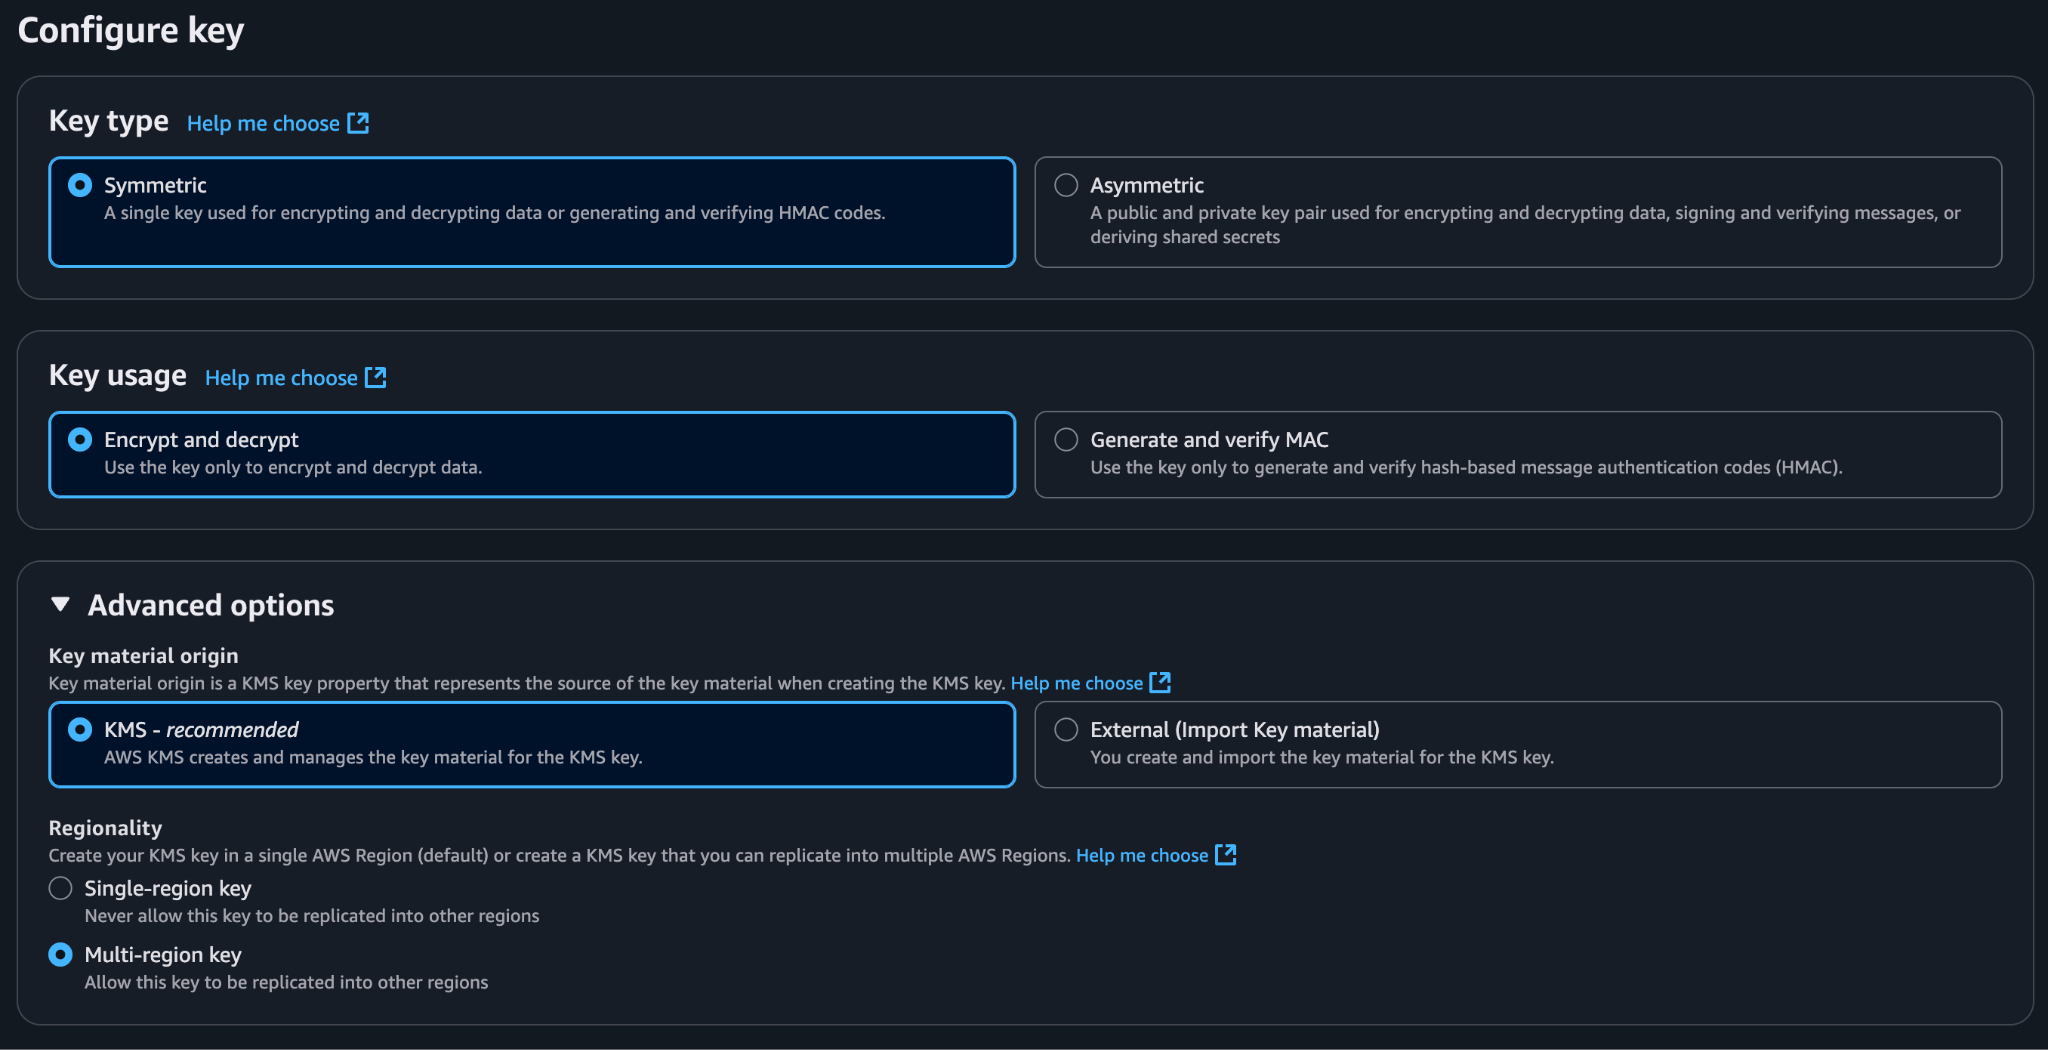
Selecting Multi-region key rules out a custom key store as the key material origin. You can still choose KMS or External (Import Key material). If you need CloudHSM or an external key store, see Single-region keys.
Step 2 — Add labels
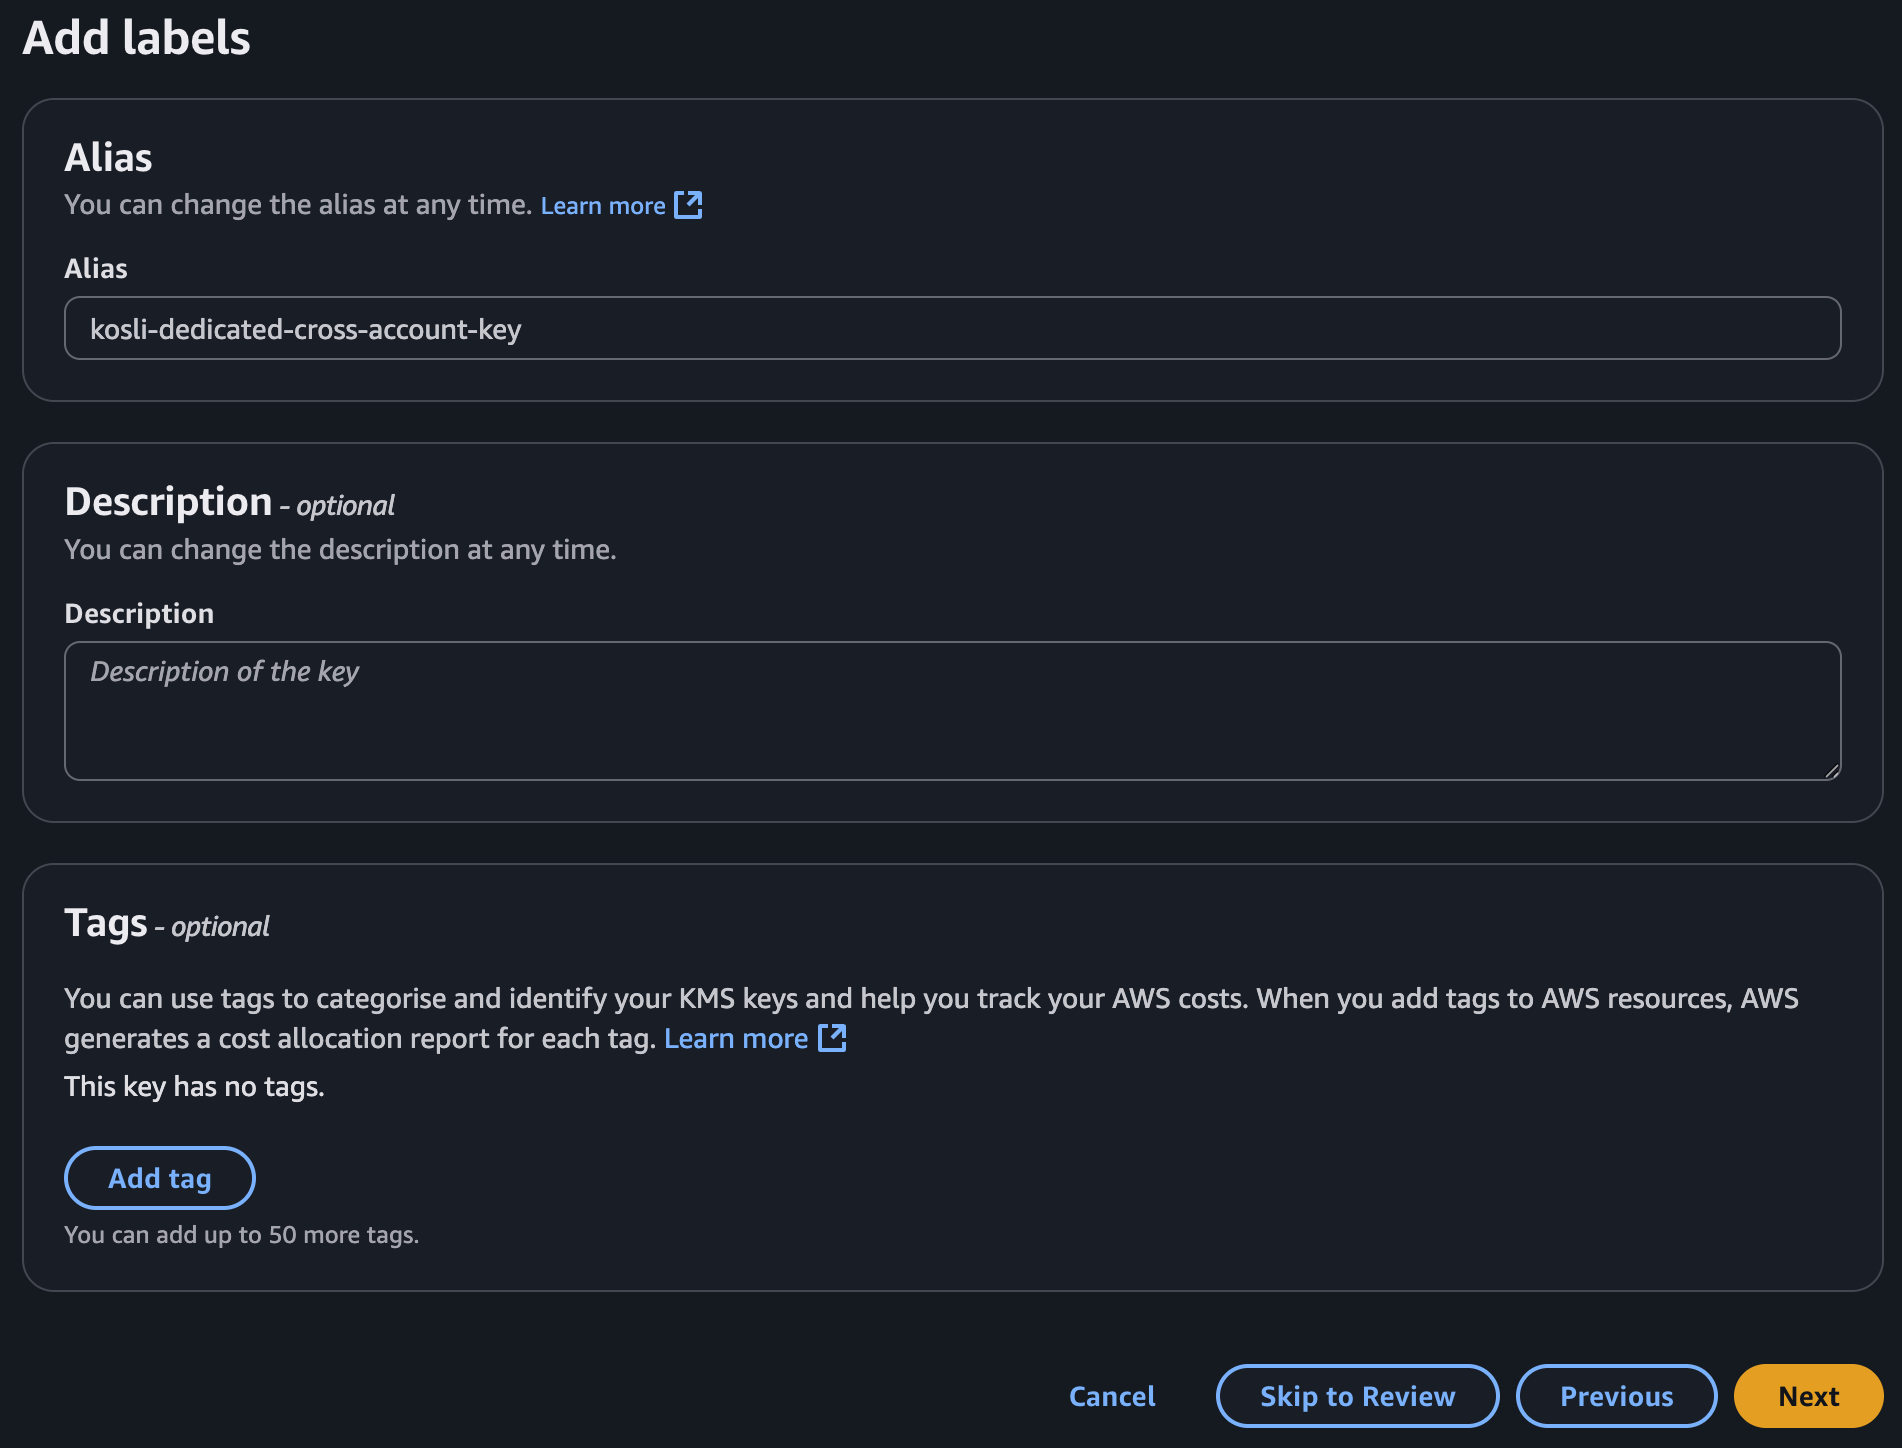
- Alias: use whatever labelling strategy your organization prefers, for example
alias/kosli-dedicated-cross-account-key. - Optionally add a description and tags to help your team.
Step 3 — Define key administrators
The key is not used from inside your AWS account, so there is usually no reason to add key administrators. To protect against accidental deletion, untick Allow key administrators to delete this key under Key deletion.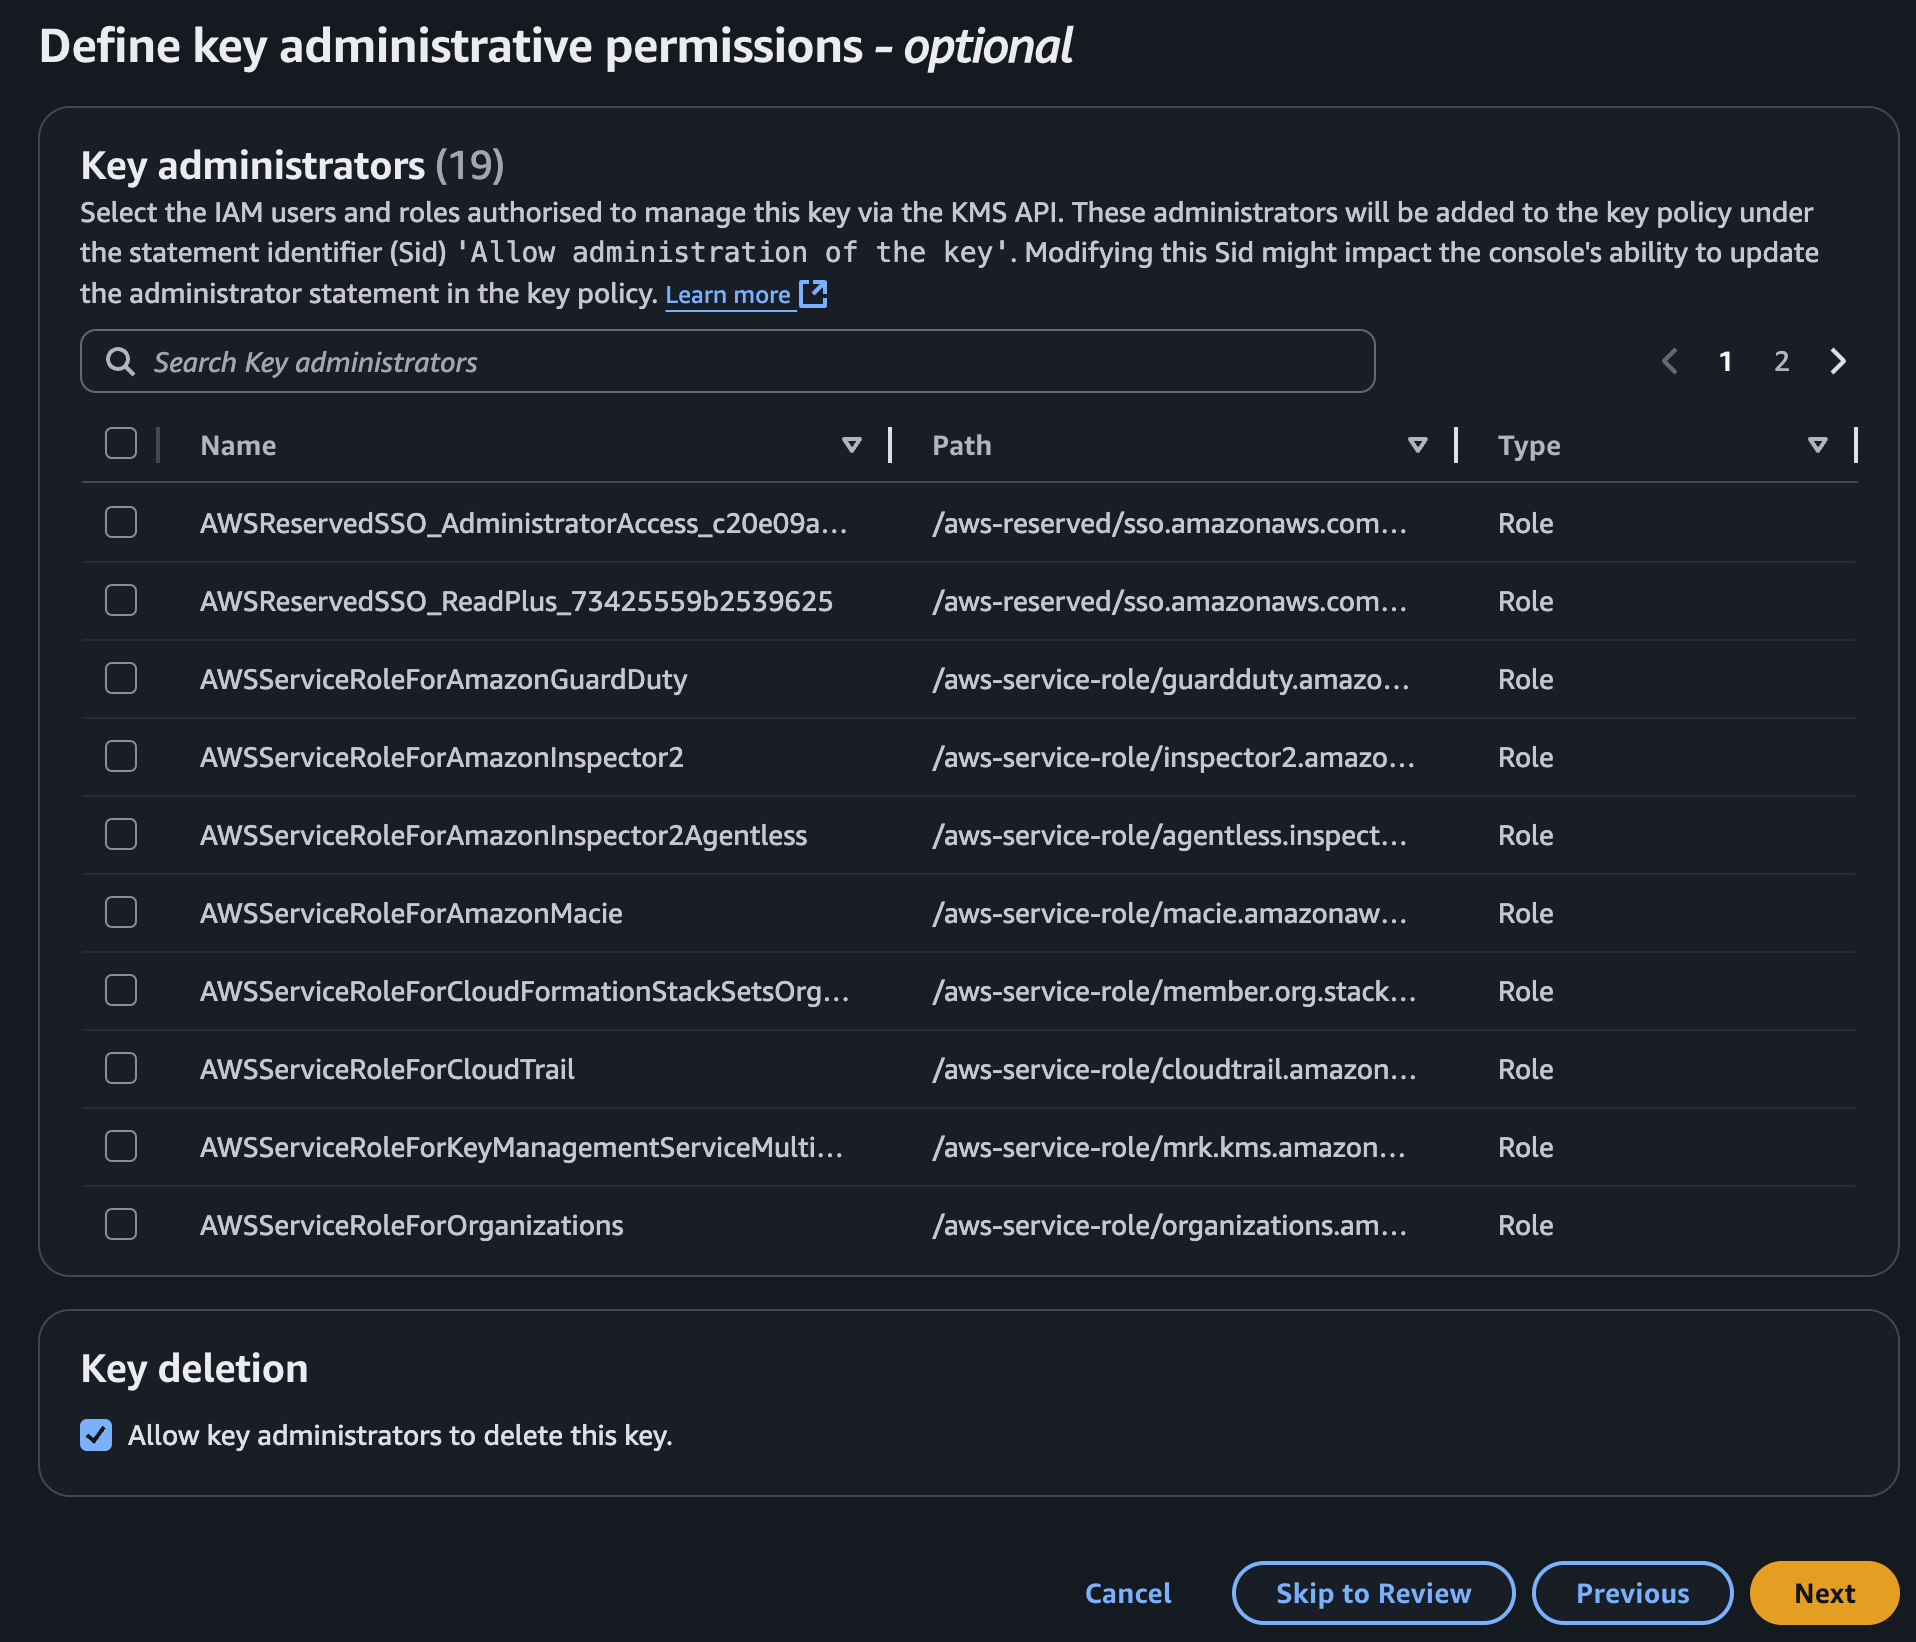
The console ticks this by default — untick it before clicking Next.
Step 4 — Define key usage permissions
The key policy is managed as JSON on the next screen, so leave the usage permissions on this page unselected. Do not add an “Other AWS account” here either — cross-account access is granted via the JSON policy.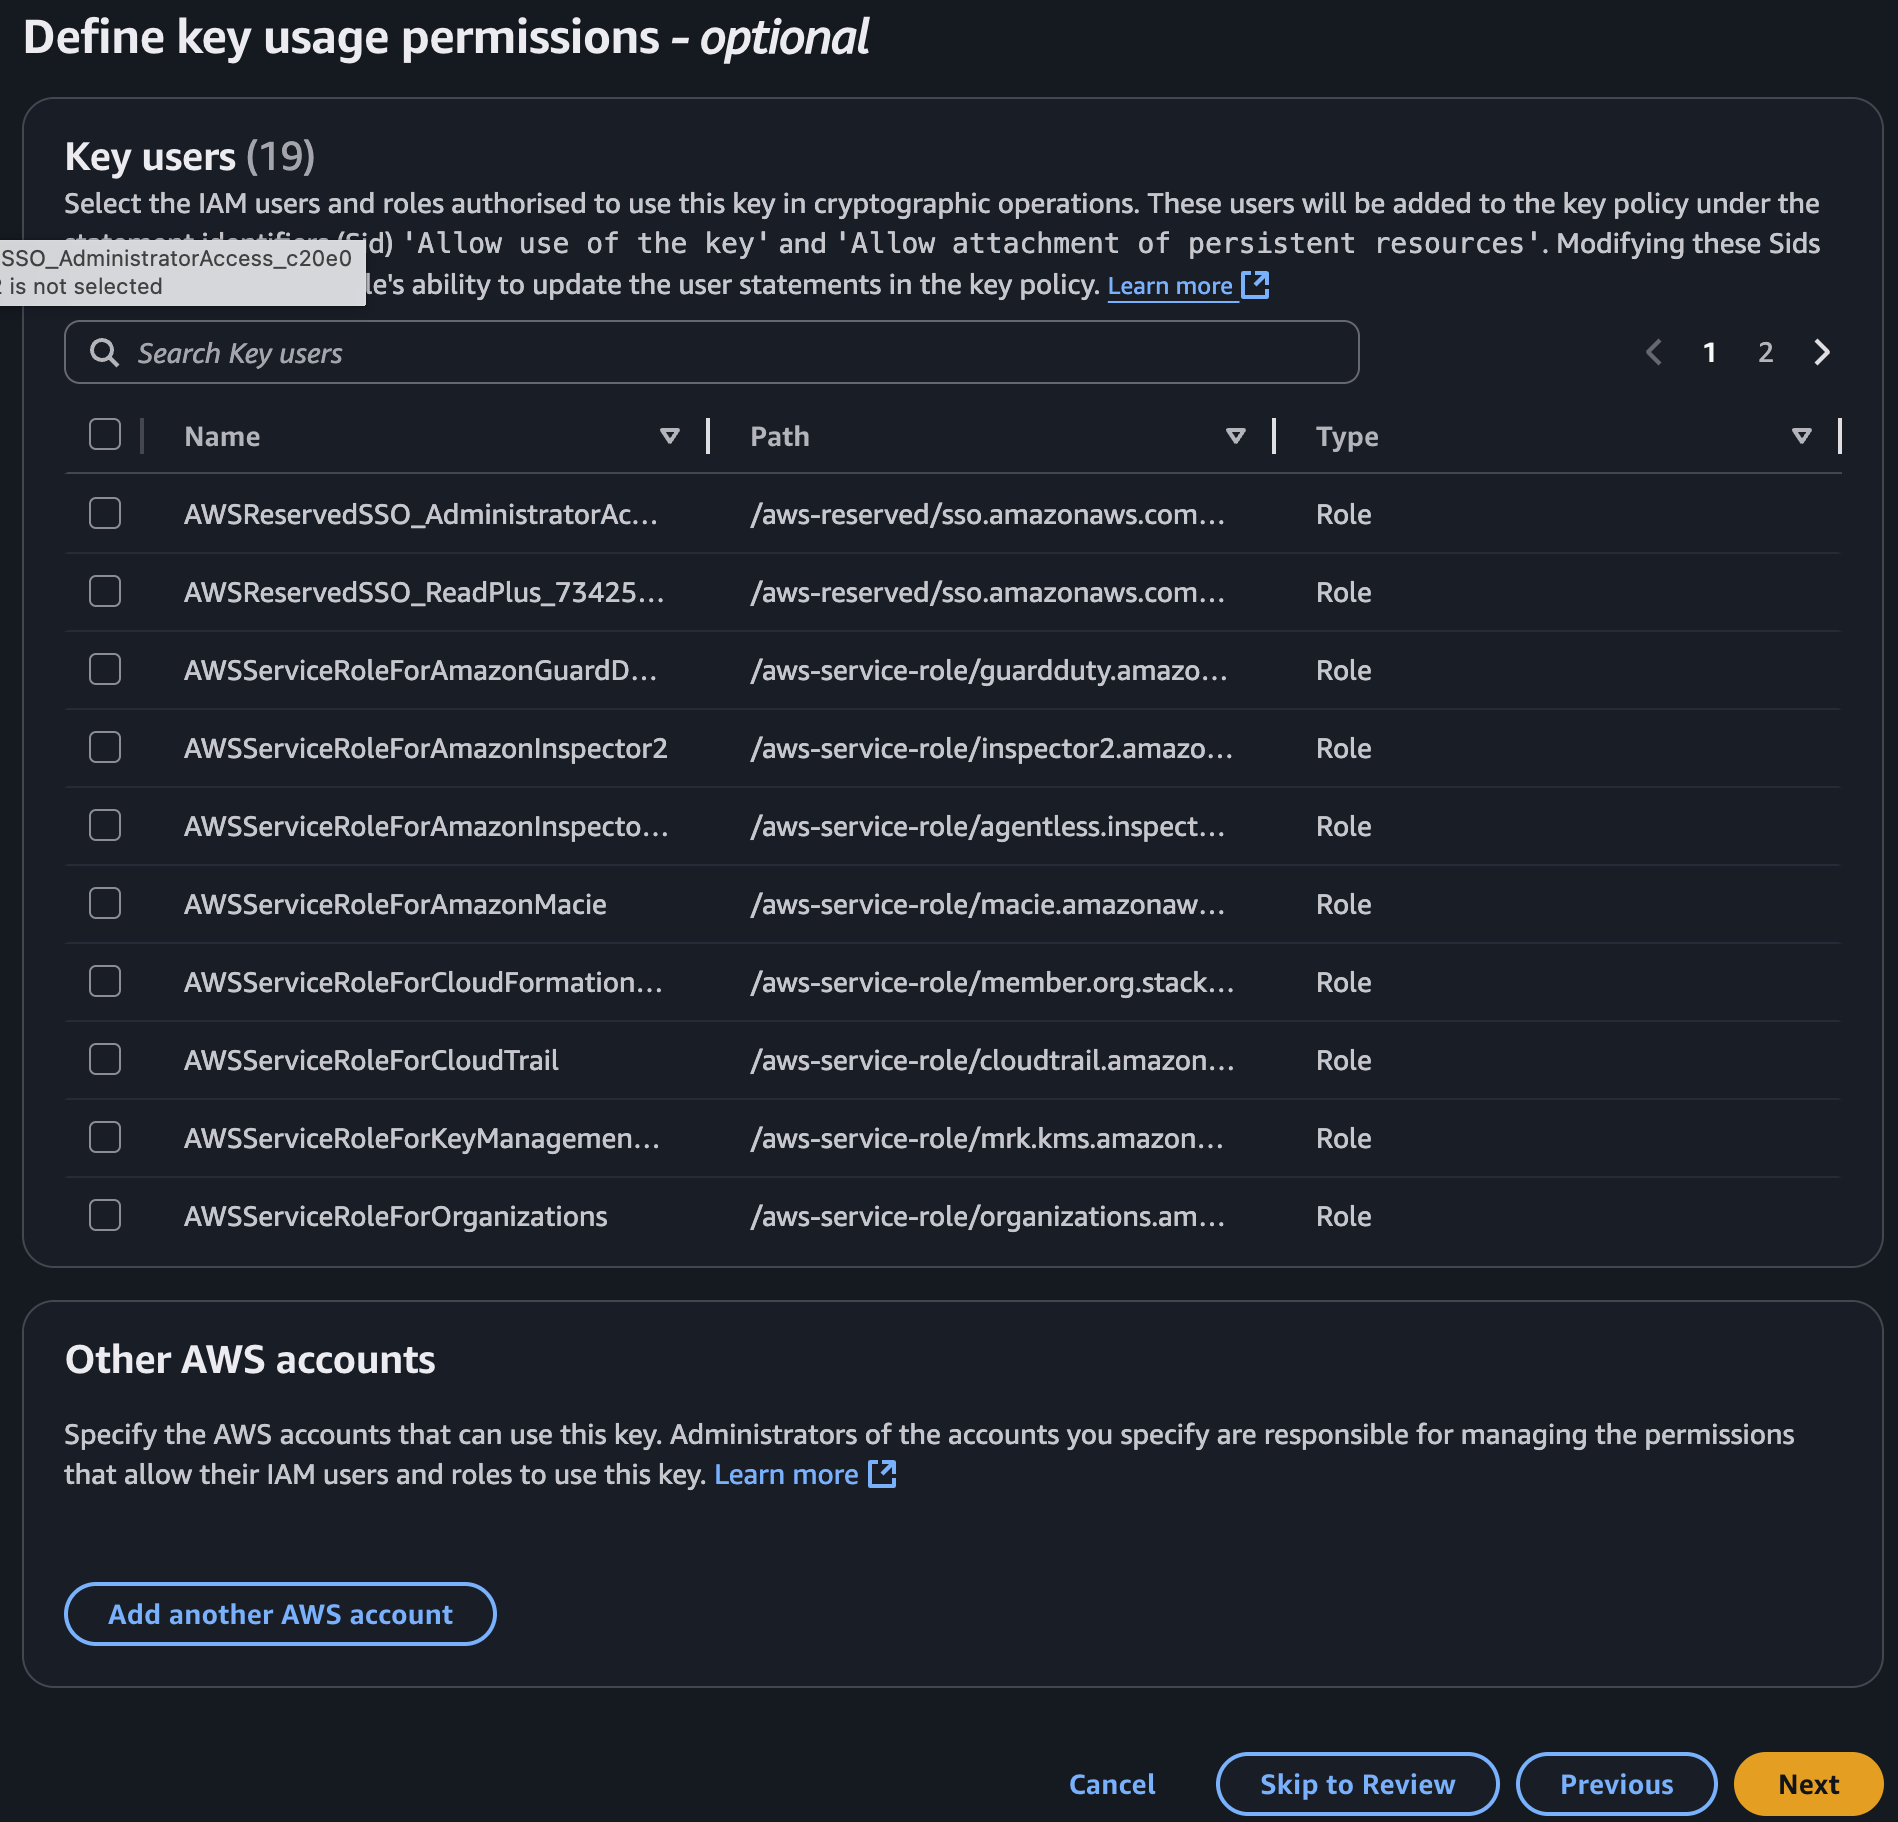
Step 5 — Edit the key policy
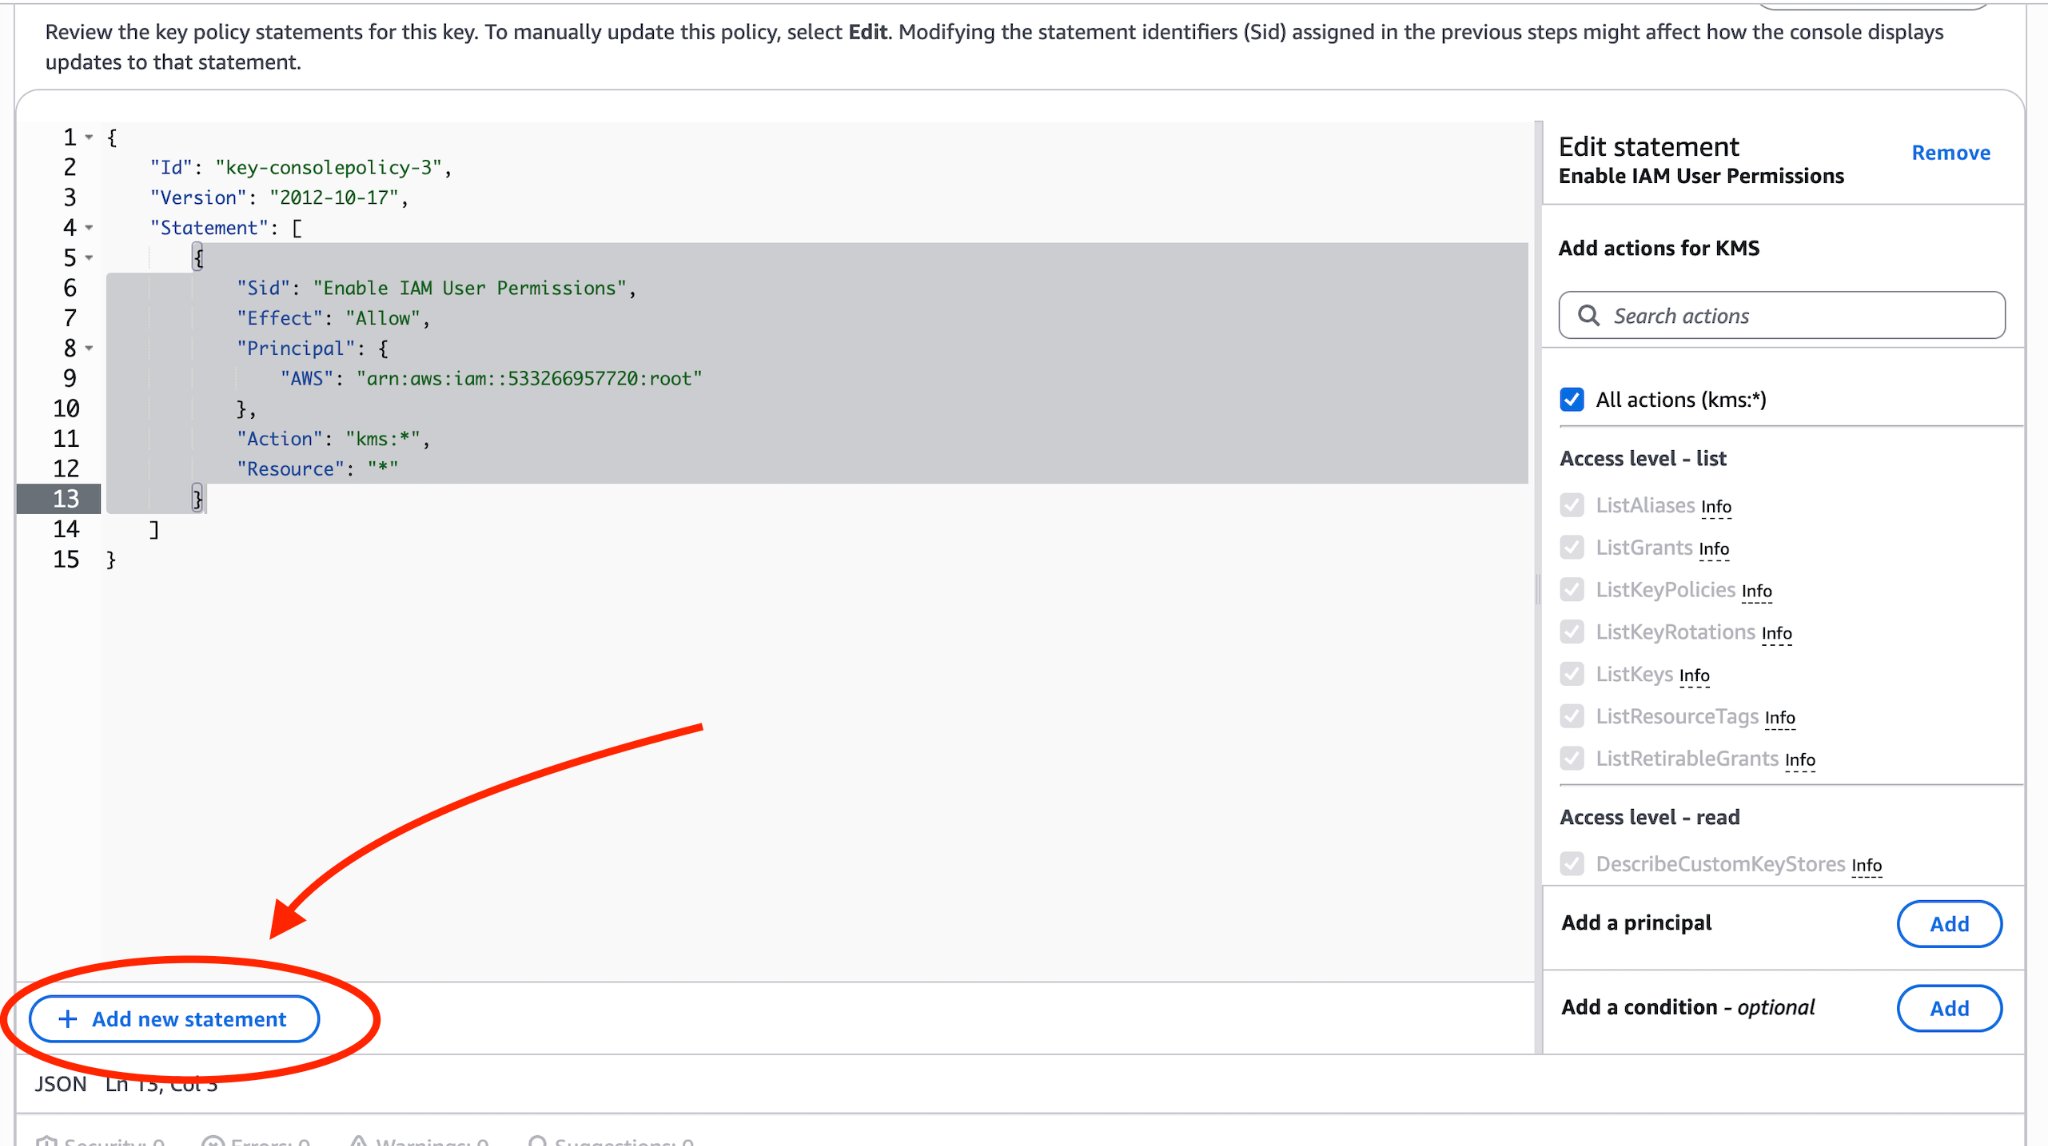
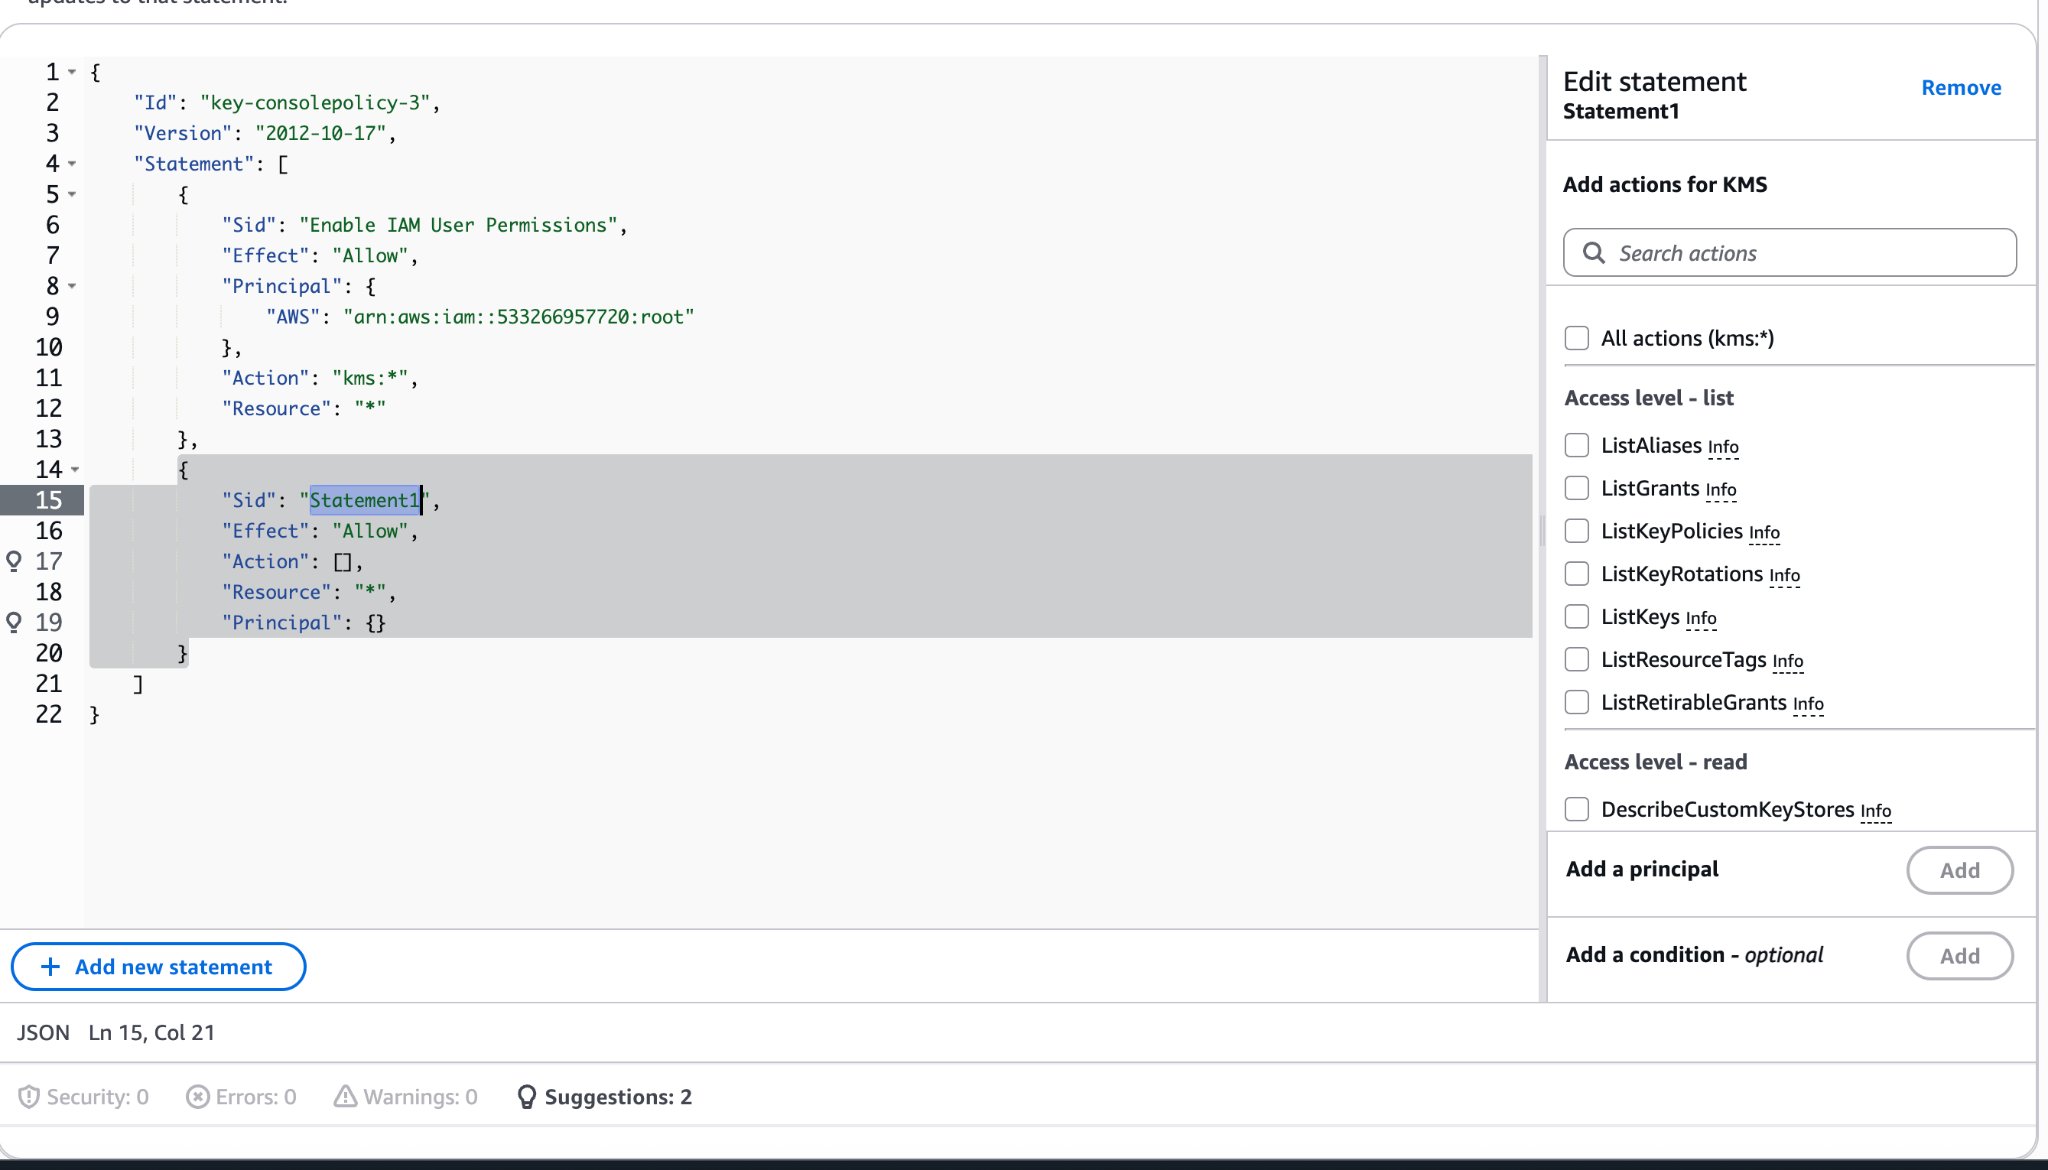
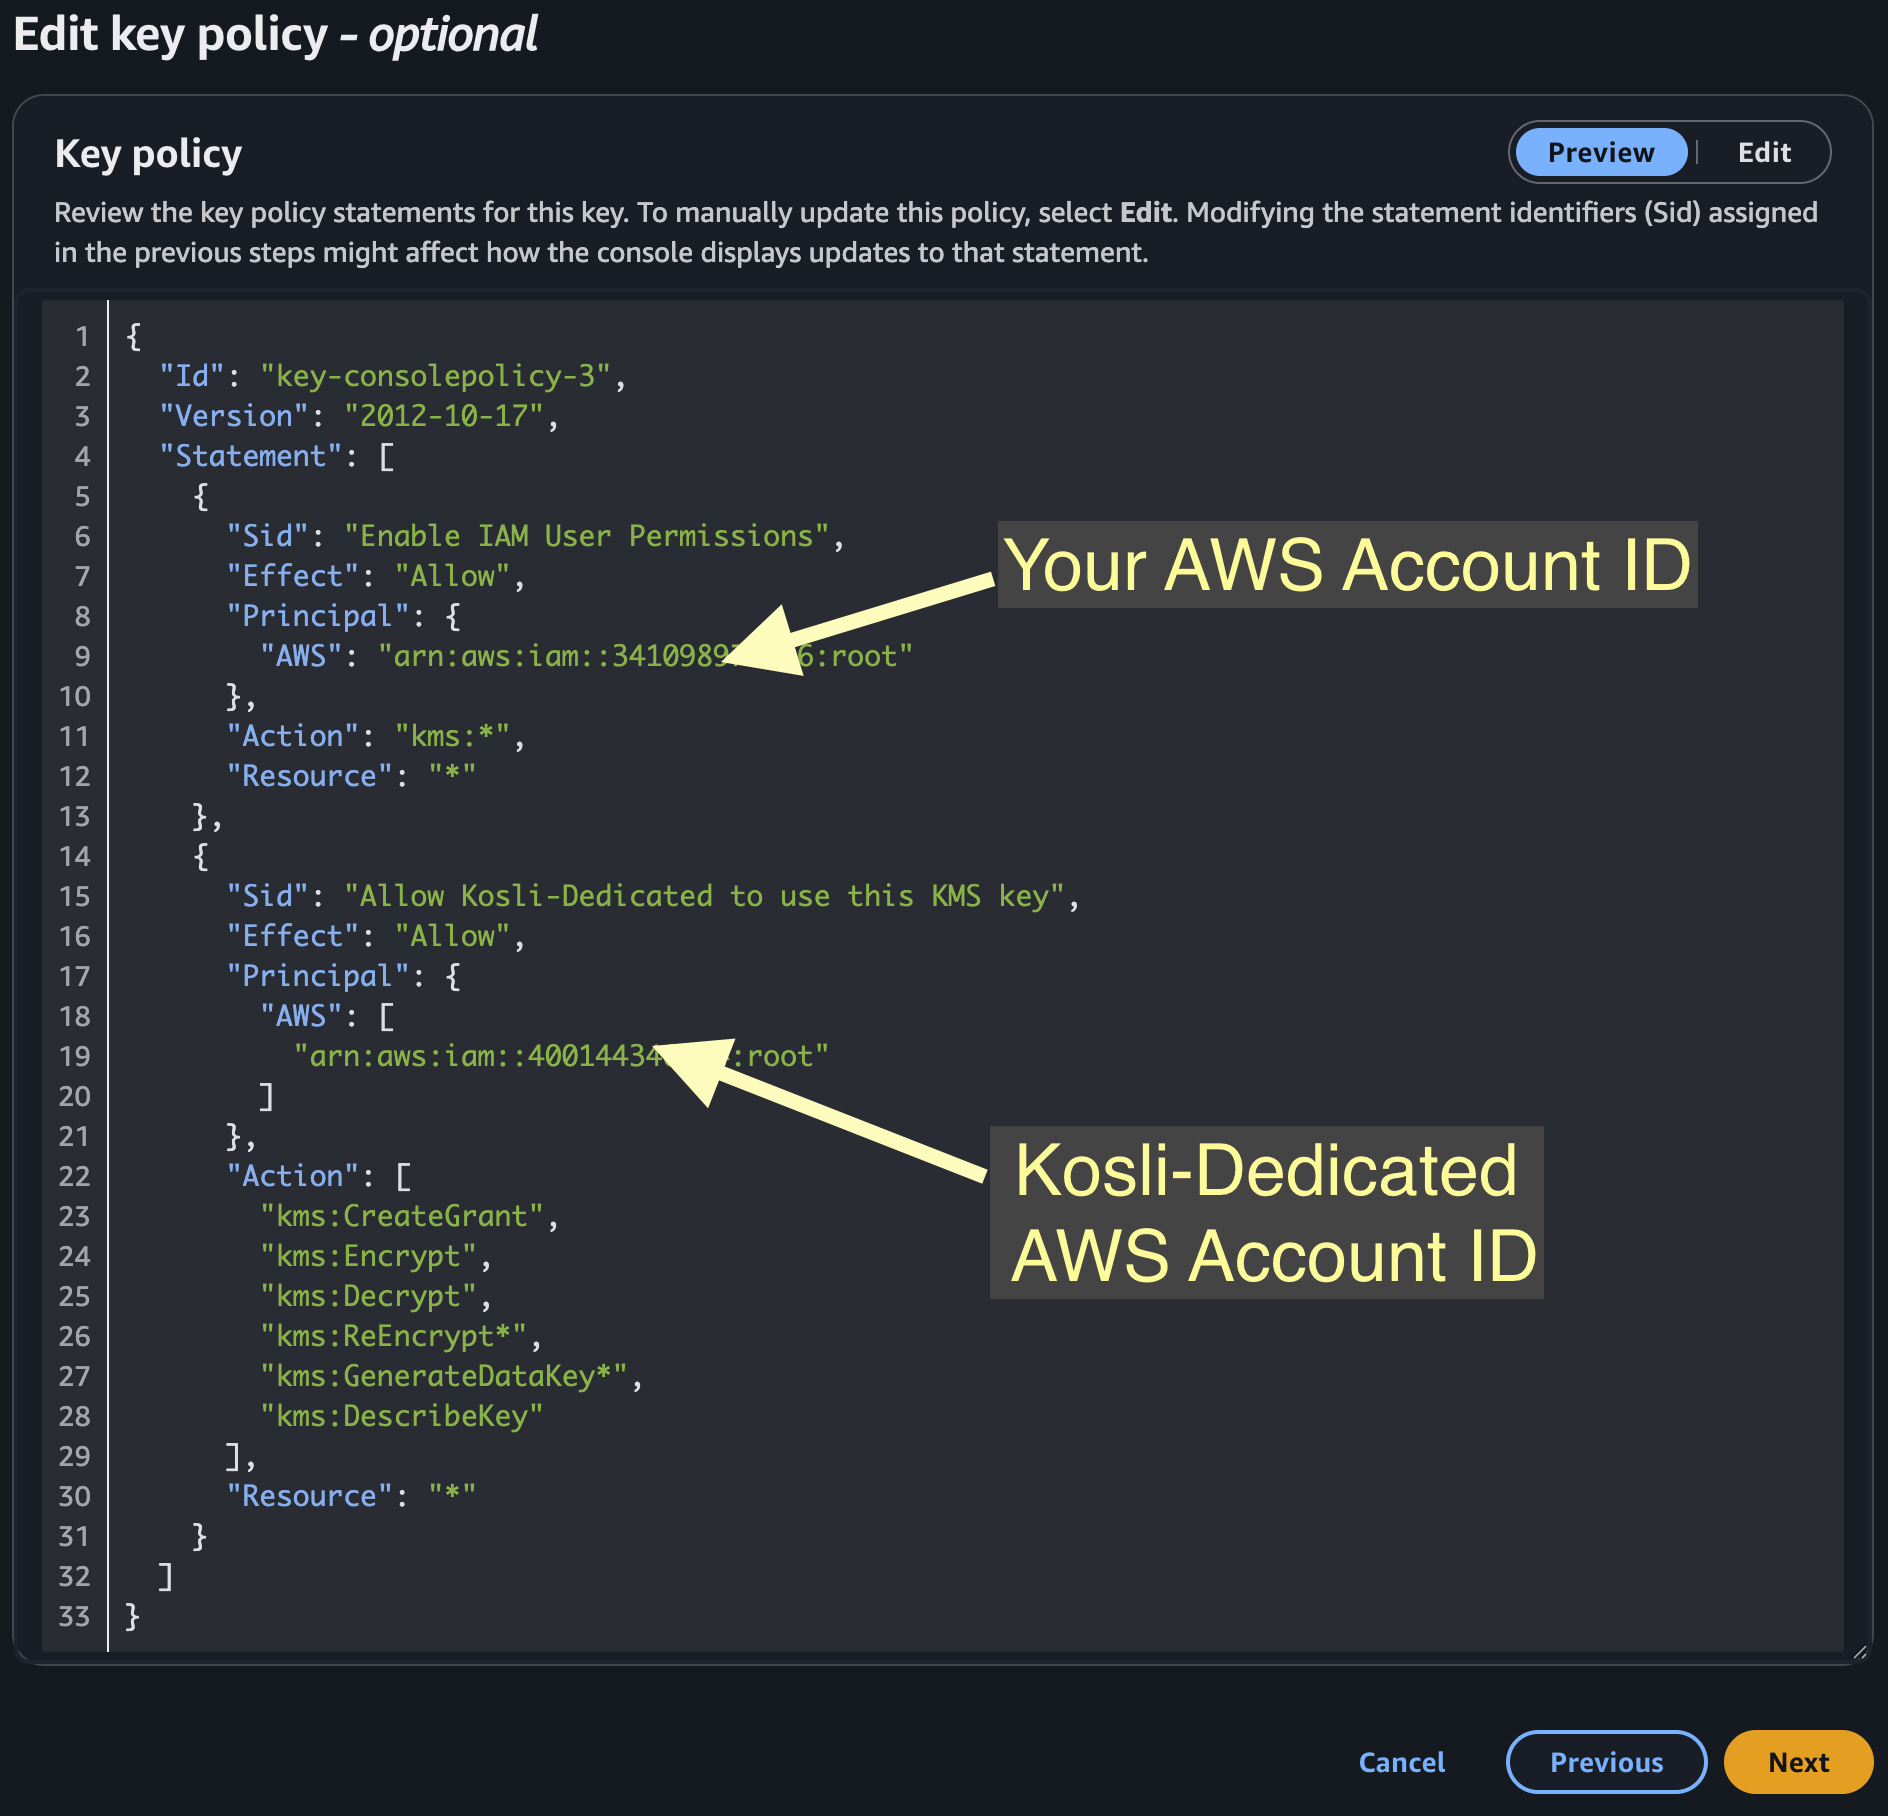
The console loads a default policy that grants access to your account root. Click Edit, then click Add new statement and add a second statement to theStatement array with the following content. A member of the Kosli Customer Success team will give you the value for <<kosli-account-id>>.
Step 6 — Review and finish
Confirm the settings match:
If anything needs changing, click Edit for that section. Otherwise click Finish to create the key. You are returned to the customer-managed keys list with the new key at the top.
Replicate the key to the secondary region
- Click the new key’s alias to open its details.
-
Select the Regionality tab. The Primary key panel shows that the key has no replicas yet.
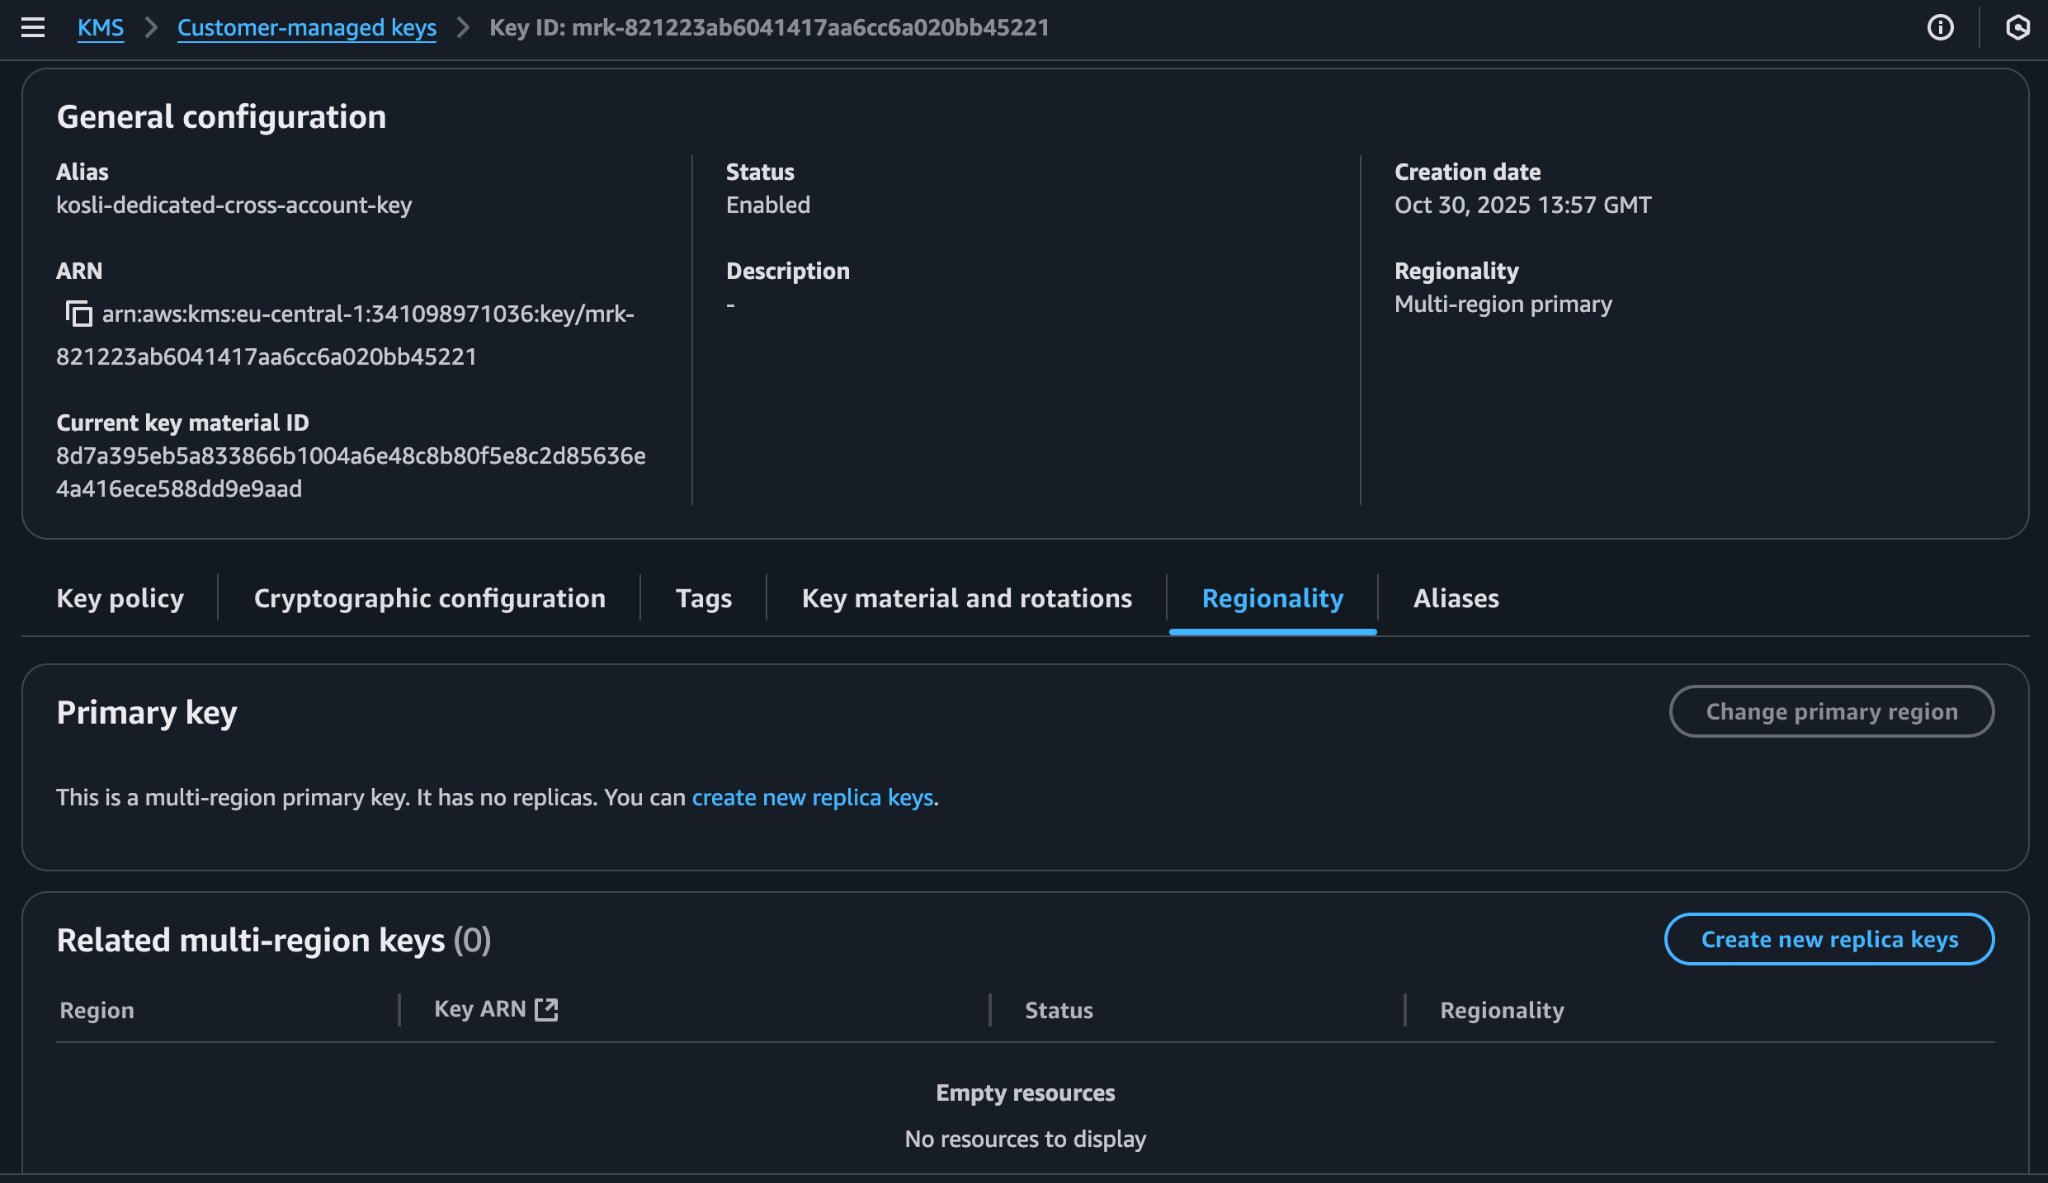
- Click Create new replica keys.
-
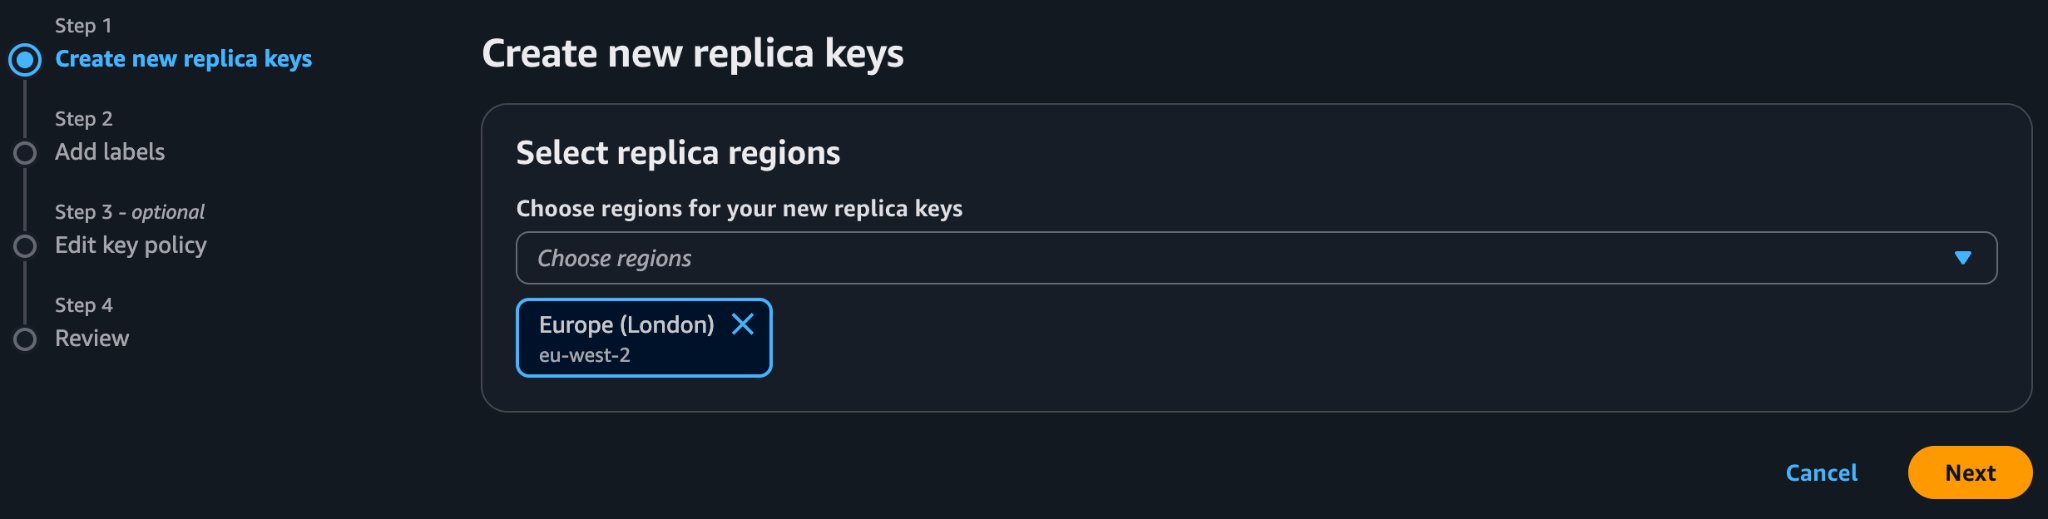
In the region dropdown (which excludes the primary region), tick the Kosli secondary region and click Next.
- The Add labels screen is pre-populated from the primary key. Change if your organization requires it, otherwise click Next.
- The console pre-populates the replica’s policy from the primary key — no changes needed. Click Next.
- Review the Confirmation message, tick the acknowledgement box, and click Create new replica keys.
Share the key ARNs with Kosli
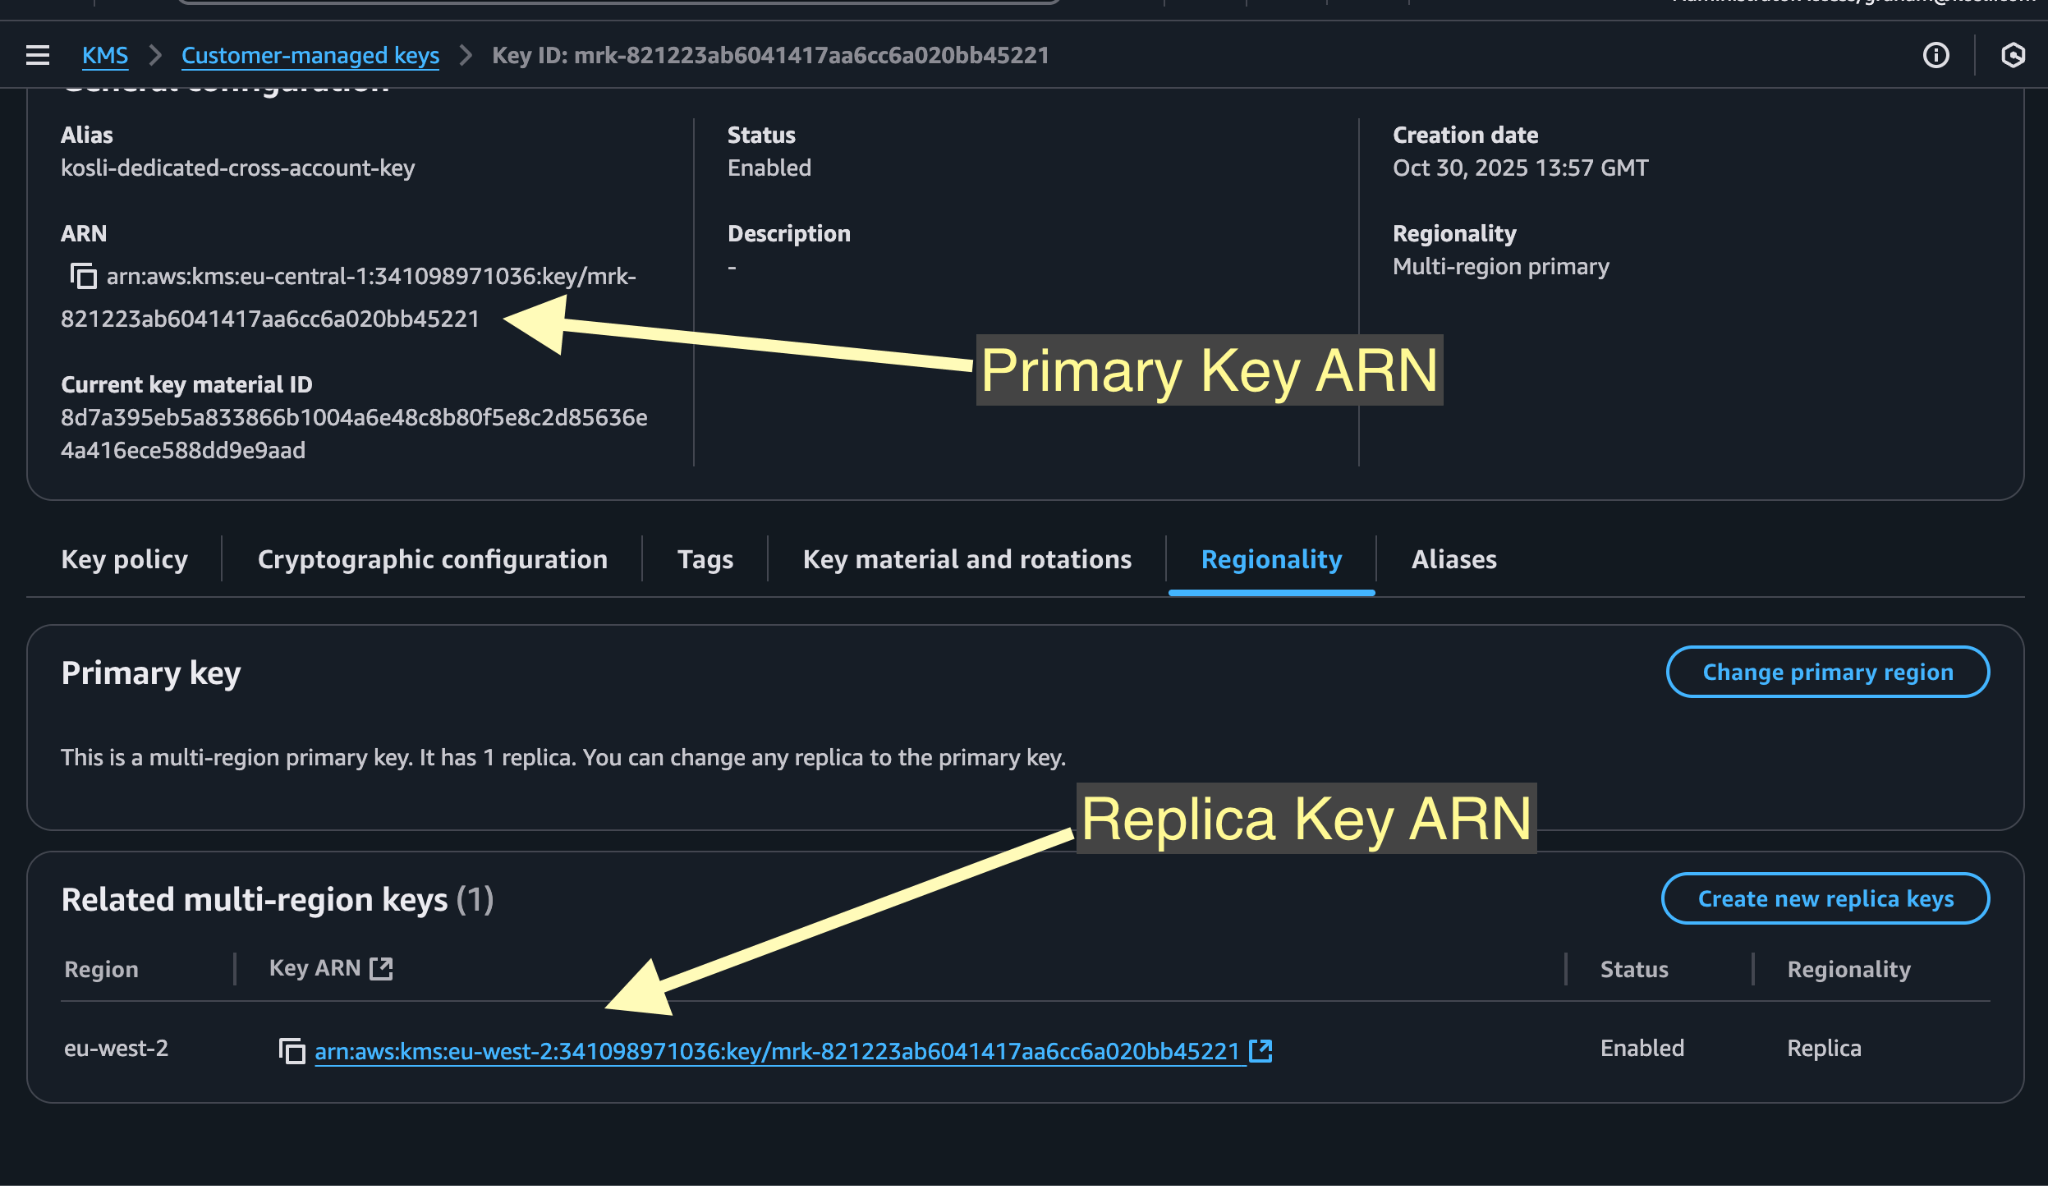
Kosli uses the primary and replica keys to encrypt data. Send both ARNs to a member of the Kosli Customer Success team:- The primary key ARN — from the General configuration panel of the primary key’s details page.
- The replica key ARN — from the Related multi-region keys panel on the same page, or from the replica key’s own details page in the secondary region.
Single-region keys
If your organization requires a CloudHSM key store (or an external key store) for the key material, create two single-region keys instead of one replicated multi-region key. The steps to create the primary key are the same as above, with two differences:- Do not tick Multi-region key under Regionality.
- Under Key material origin, select your CloudHSM key store (or external key store) rather than KMS.
Terraform example
The following is the minimum Terraform needed to create the multi-region key and its replica for Kosli Dedicated. Setprimary_aws_region, secondary_aws_region, and kosli_dedicated_account_id for your instance.
This example uses the top-level
region argument on aws_kms_key, aws_kms_alias, and aws_kms_replica_key, which requires AWS provider v6.0 or later. On earlier versions, use aliased provider blocks instead.